
[ad_1]
If you happen to’ve ever been to Cisco Dwell and seen the sales space with a show so that you can decide locks, then in regards to the Cisco Superior Safety Initiatives Group (ASIG). We’re chartered with safety testing and moral hacking for all Cisco services, whether or not within the cloud or on-premises. Something Cisco sells, we now have a go at it and attempt to break it—discovering vulnerabilities as early as potential—earlier than it’s deployed on the web and reaches buyer environments.
Our Product Safety Incident Response Staff (PSIRT) distributes info about found vulnerabilities to assist harden Cisco choices. In case you have a weak situation, studying how you can exploit these vulnerabilities in a community may show you how to decide what mitigations to use and strengthen your safety posture.
Changing into a Hacker
Yearly, we now have a category referred to as Changing into a Hacker, which teaches college students how you can ethically hack right into a simulated community to allow them to learn to shield it. It’s primarily for interns from faculties and excessive colleges concerned in cybersecurity research.
The Changing into a Hacker course offers college students publicity to a real-world community (utilizing Cisco Modeling Labs [CML]). This simulated community acts extra like what they might see on-premises, utilizing bodily switches, routers, and firewalls. Cloud networks are usually extra locked down (rightly so) and behave otherwise. Changing into a Hacker additionally includes a simulated Wi-Fi community, so college students get uncovered to numerous community sorts. We plan to have cloud targets within the Changing into a Hacker lab finally, so the scholars could have a mix of digital on-prem and in-cloud targets, getting the most effective of each worlds.
Changing into a Hacker has not too long ago turn out to be public, so anybody can entry the course supplies by way of Github. In fact, we don’t make the CML net interface public for safety causes, however we will shortly take it down and begin it again up at scale.
Whereas Changing into a Hacker is created by volunteers and isn’t an official Cisco product, it does present an incredible place to begin for purchasers who wish to create their very own hacker coaching eventualities utilizing a cloud account.
How a community hacking course can educate community safety
A course on moral hacking, also referred to as penetration testing or white-hat hacking, is essential for firms in the long term, serving to them establish and repair vulnerabilities earlier than malicious hackers can exploit them, thus strengthening the community in opposition to future assaults. Coaching in moral hacking can even assist firms adjust to safety rules and lower your expenses, avoiding the price of authorized charges, fines, and enterprise loss from knowledge breaches. General, this type of coaching improves safety consciousness all through the group, main to higher safety insurance policies and coaching for workers to assist them acknowledge and reply to potential threats.
The premise is that if you engineer one thing to be safe, you need to be taught to interrupt it. That means, you’ll know what to search for inside your individual networks. A typical discovering is an OS command injection vulnerability, an internet vulnerability wherein the attacker makes use of present APIs to execute arbitrary code by tacking on an extra working system command utilizing particular characters.
One instance is an internet interface that means that you can ping a bunch so you’ll be able to affirm reachability by that net interface, which can enable these characters to execute instructions apart from a ping. Once you perceive the sort of injury a hacker can do to your community, you’ll be able to higher perceive the criticality of defending it.
Working with Cisco Modeling Labs for extra open coaching
Recently, we’ve been working with the CML group for Cisco’s inside coaching, which lets our moral hackers use CML to do safety testing for each Cisco product. Nevertheless, what began as a non-public mission is popping right into a probably important alternative for an open-source resolution.
It’s a wholly totally different means of constructing a community so as to do offensive safety testing. We’ve been operating it in Google Cloud, and it’s working nice.
Cisco Modeling Labs deployment within the Google Cloud platform
We’ve been utilizing examples of Terraform configurations on DevNet. These configurations mean you can take the CML picture typically supplied as an ISO picture or utility bundle and cloudify it for set up in Amazon Internet Companies (AWS) or Microsoft Azure. Terraform is a software for outlining and managing IT infrastructure utilizing code, or infrastructure as code (IaC). IaC makes it simpler to arrange, replace, and scale your sources constantly and effectively.
Whereas that was working effectively, we quickly realized that to run it on the scale we wanted, we must run CML on a couple of bare-metal machine in a cluster in AWS—and that will get costly. We additionally required that every lab may settle for connections from the Web and provoke connections to the Web with IPv4 and IPv6 utilizing distinctive addresses. We discovered that the Google Cloud Platform met our wants properly.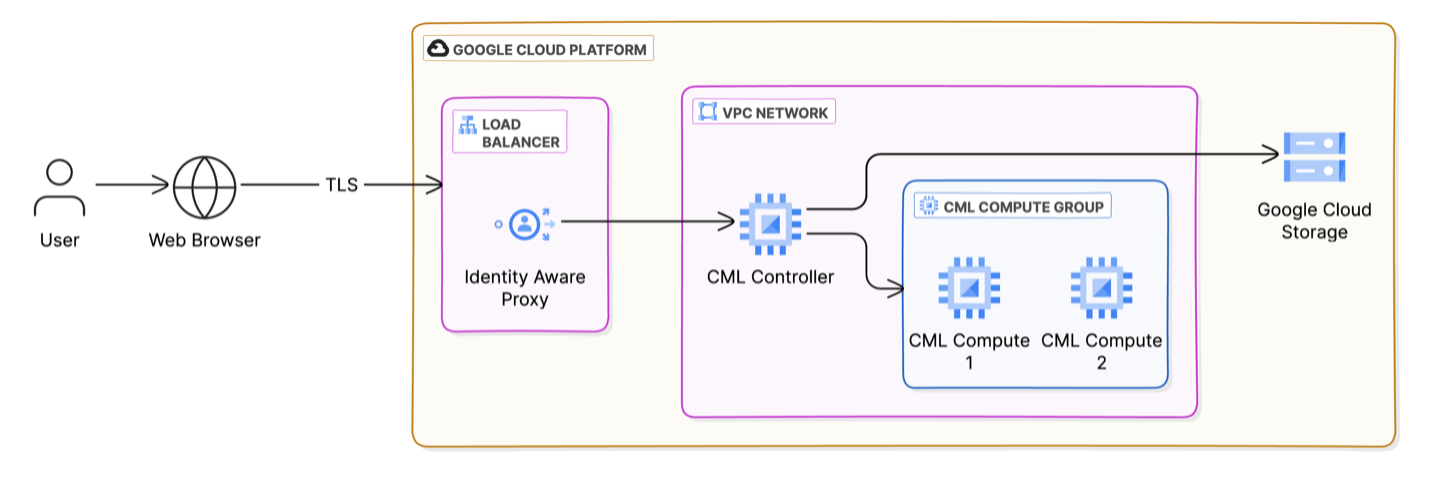 CML runs its personal hypervisor, which is software program that enables a single laptop to run a number of digital machines (VMs) concurrently. The hypervisor is a safety measure.*
CML’s open-source hypervisor relies on Linux Kernel-based digital machine (KVM) and libvirt, a toolkit to handle virtualization platforms. It means that you can run digital machines on server {hardware} just like the Cisco Unified Computing System (UCS). This CML hypervisor can run nested on digital machine situations within the cloud and run digital machines by itself to help our labs.
Cisco Modeling Labs workbench interface
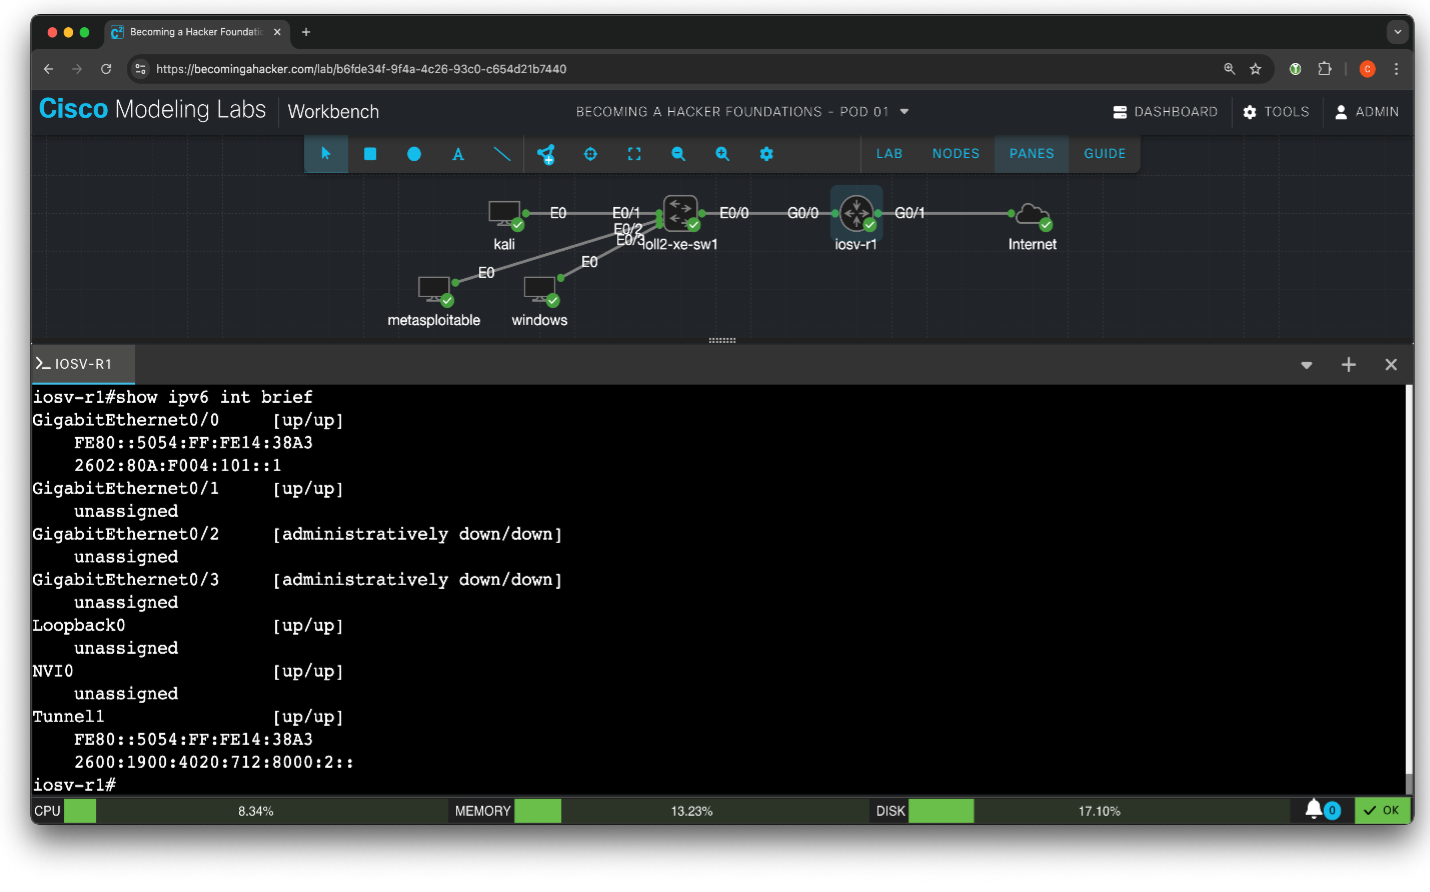
By taking this course with CML, customers connecting remotely with an internet browser will get their very own pod (a bunch of digital, exploitable machines). And because it’s been working so effectively for our inside groups, the CML group was agreeable once I provided to jot down the Terraform modules to make use of Google Cloud Platform to increase our coaching.
I hope to doc a Google Cloud deployment and combine these adjustments into the primary DevNet repository quickly.
Changing into a Hacker lab deployment
We wish to make this technique of provisioning labs for coaching extra common. The Changing into a Hacker Foundations course is the primary iteration of this technique. We additionally provide different cybersecurity courses internally, however none use CML… but.
As a result of CML means that you can interface from anyplace, you’ll be able to entry your CML occasion on the cloud and do testing. It’s so compelling to make use of as a result of it’s all automated.
For instance, once we run a Terraform command, 20 pods (virtualized labs) are prepared to be used. We have now all of the configs to deploy it you probably have a CML subscription. Whereas not the entire photos are totally public as a result of it has a licensed Home windows picture, a consumer may simply create their very own photos not supplied out-of-the-box.
We hope to increase this course over time. Keep tuned for more information on this nice alternative for Cisco coaching and CML that will help you be taught extra hacking ideas and tips to higher safe your community.
NOTE: Cisco Modeling Labs is a industrial and formally supported product from Cisco. Be taught extra
Join Cisco U. | Be a part of the Cisco Studying Community.
Observe Cisco Studying & Certifications
X | Threads | Fb | LinkedIn | Instagram | YouTube
Use #CiscoU and #CiscoCert to hitch the dialog.
*How we safe the Changing into a Hacker course
There’s no vulnerability in Cisco Modeling Labs (CML) that we all know of, however we’re deploying a lab (pod) that has gadgets in it which can be weak. CML means that you can make a networking topology, not just for routers but in addition for servers and hosts. You possibly can deploy a Linux or Home windows machine into it. It’s all based mostly on a kernel-based digital machine (KVM), a virtualization expertise that turns a Linux machine right into a hypervisor, permitting a number of remoted digital environments to run on a single host machine.
Hypervisors are vital to the safety of virtualized environments, particularly should you run machines that may execute weak code. Some necessary methods hypervisors handle safety embrace:
- Isolating digital machines (VMs) from one another ensures that if one VM is compromised, the attacker can not simply entry different VMs (which include identified weak code) or the host system.
- Controlling allocating {hardware} sources (CPU, reminiscence, storage, and community) to VMs to forestall useful resource exhaustion, the place one pupil lab can overload others.
- Imposing strict entry management insurance policies so solely approved customers and processes can work together with the VMs and the hypervisor itself, so college students solely see their digital machines and never others.
- Implementing digital community safety measures, corresponding to digital firewalls and community segmentation, to guard VMs from network-based assaults.
- Sandboxing VMs to restrict their skill to work together with the host system and different VMs.
Listed here are a couple of different safety measures we use for our Changing into a Hacker web site:
- We isolate the positioning from the remainder of Cisco, which is one motive it’s necessary to run CML within the cloud. If one thing had been to occur, we may shortly destroy the deployment and recreate it. Nevertheless, if this had been operating deep inside a Cisco lab, that might be tougher and would possibly hurt Cisco’s company community.
- We shield the positioning with sturdy passwords generated throughout lab creation and multifactor authentication (corresponding to Duo) utilizing the Id Conscious Proxy, which may also be turned on and off relying on the category’s viewers.
- Whereas the lab has free entry to the Web, its velocity is restricted; every pod can solely transmit a couple of megabits per second.
- We preserve Area Identify Service (DNS) and move logs of individuals’s actions throughout the community.
- Each pod has a novel IP handle, which we will hint to particular person college students.
Exploring AAA and TACACS Configuration with Cisco Modeling Labs
Share:
[ad_2]
Leave a Reply